alexander
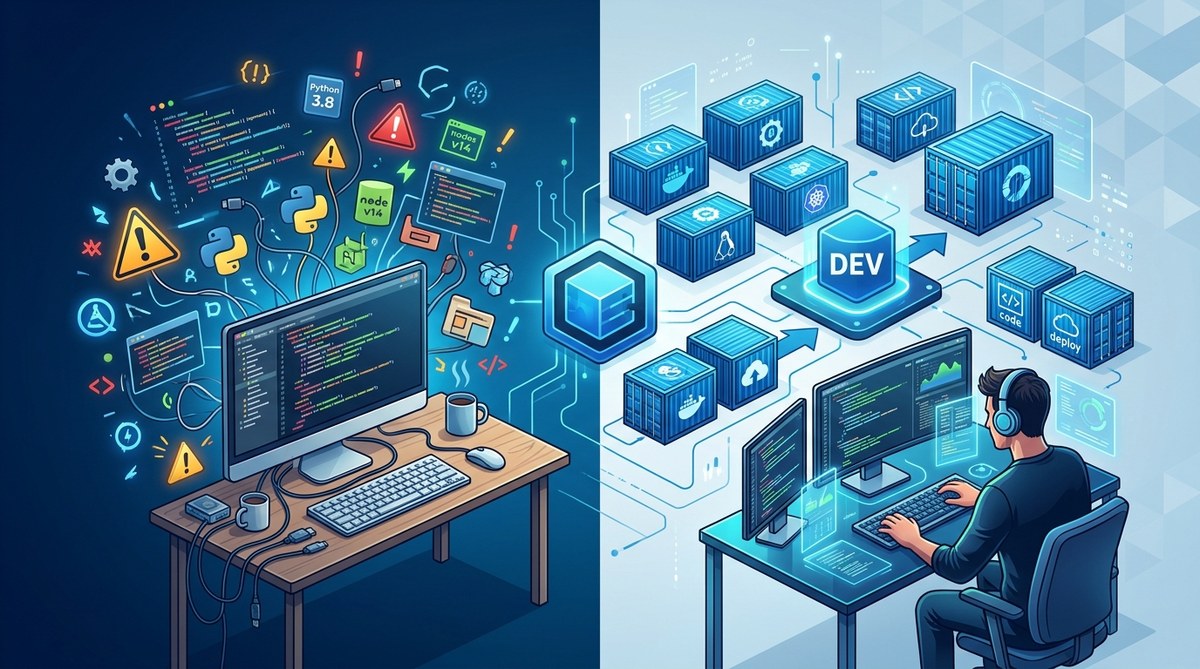
You are debugging a Node.js service at 2 AM. The logs look fine on your laptop, but your teammate’s machine throws a cryptic error about a missing OpenSSL version. You check the ticket system, and three other developers have the same problem. The root cause? Environment drift. Everyone installed different system libraries, and nobody wrote them down.
This is the exact moment you realize that your development environment needs a container strategy. Not just one Dockerfile thrown into the repo. A real, intentional approach to how your team builds, shares, and maintains containerized workspaces. A solid development environment container strategy eliminates the “works on my machine” problem and turns your local setup into a repeatable, reliable tool.
A dedicated container strategy for your development environment is not about running Docker Compose once. It is about standardizing how every team member builds, tests, and ships code. This article walks you through the core decisions: choosing base images, managing dependencies, handling secrets, and integrating with your CI/CD pipeline. You will leave with a repeatable plan that cuts onboarding time and eliminates environment-related bugs.
Why a Sporadic Container Setup Fails
Many teams try containers halfway. A developer writes a Dockerfile for a new microservice, pushes it, and forgets about it. Another developer modifies it locally, commits a broken image, and the team spends an afternoon untangling the mess. This approach is worse than no containers because it gives a false sense of consistency.
A container strategy is the difference between a tool and a toy. It provides rules for:
- Base image selection. Which Linux distribution do you standardize on? Alpine, Ubuntu, or Debian?
- Dependency pinning. Are you locking exact versions of system packages, or letting apt get the latest?
- Volume mounts vs. copying code. When do you use bind mounts for live reload, and when do you copy the source into the image?
- Secrets management. How do you pass API keys and database credentials without hardcoding them in the image?
Without these rules, your team will eventually face a situation where one developer’s container works and another’s does not. The strategy turns that chaos into a predictable process.
The Core Components of a Development Environment Container Strategy
A complete strategy covers four areas. Think of these as the legs of a table. If one is weak, the whole setup wobbles.
1. Image Standardization
Choose a single base image for your primary runtime. If you use Python, decide between python:3.12-slim-bookworm and python:3.12-alpine. Document that choice in a shared wiki or a README. Then create a base image that includes your team’s common tools: git, curl, jq, a code formatter, and any debugging utilities.
“A team that standardizes on one base image eliminates 80% of environment-related bugs before they happen. The remaining 20% usually come from unmanaged dependencies.” — Sarah Chen, Senior DevOps Engineer at a Series B startup
2. Dependency Management
Do not install dependencies inside the container by hand. Use a lockfile. Whether it is package-lock.json, requirements.txt, or Gemfile.lock, the lockfile ensures that every developer gets the same versions. Your Dockerfile should copy the lockfile first, install dependencies, and then copy the rest of the source code. This layer caching strategy speeds up rebuilds significantly.
3. Development vs. Production Images
Your development container needs different things than your production container. In development, you want hot reloading, debuggers, and test databases. In production, you want minimal size and no build tools.
| Component | Development Container | Production Container |
|---|---|---|
| Base image | Full OS with build tools (e.g., python:3.12) |
Slim variant (e.g., python:3.12-slim) |
| Dependencies | Dev + test packages | Only runtime packages |
| Source code | Mounted as a volume | Copied into image |
| Debugging tools | Included (gdb, strace, lsof) | Excluded |
| Ports | Exposed for debuggers | Only application port |
4. Secrets and Configuration
Never bake secrets into an image. Use environment variables with .env files that are gitignored. For more advanced setups, integrate with a secrets manager like HashiCorp Vault or a cloud provider’s secrets service. Your strategy should specify a single method for passing secrets to the container, such as Docker Compose’s env_file directive.
A Practical Process for Implementing Your Strategy
Follow these steps to move from theory to practice. Each step builds on the previous one.
-
Audit your current setup. List every service your team runs locally. Note which ones already have Dockerfiles and which ones rely on manual installation. Identify the biggest pain points: slow builds, missing dependencies, or conflicting versions.
-
Choose a base image standard. Pick one distribution for your primary stack. For most teams, Debian-based images (Ubuntu or Debian) are the safest choice because they have the largest package ecosystem. Document the exact tag (e.g.,
ubuntu:24.04) and create a Dockerfile that adds your common tools. -
Build a shared base image. Push this image to a private registry like Docker Hub, GitHub Container Registry, or Amazon ECR. Tag it with a version number. When you update the base image, bump the tag and notify the team.
-
Create a Docker Compose template. Write a
docker-compose.ymlthat defines all services for local development. Include databases, message queues, and caching layers. Use named volumes for persistent data so that restarting the container does not wipe your test database. -
Integrate with your CI/CD pipeline. Your CI system should build the same images you use locally. This ensures that the “it passed on my machine” and “it passed on CI” are the same thing. Use the Why Integrating a CI/CD Pipeline Is Non-Negotiable in 2026 guide to tighten this integration.
-
Document the workflow. Write a short README that shows how to start the environment, run tests, and debug. Include common commands like
docker compose up -d,docker compose exec app bash, anddocker compose down. Keep it under 200 words so people actually read it.
Common Mistakes and How to Avoid Them
Even with a strategy, teams slip up. The table below lists the most frequent mistakes and their fixes.
| Mistake | Why It Hurts | Fix |
|---|---|---|
Using latest tag for base images |
Builds become non-deterministic | Pin to a specific digest or version tag |
| Installing packages interactively | Containers fail in CI | Use a Dockerfile or a setup script |
| Storing secrets in the image | Anyone with the image can extract them | Use .env files or a secrets manager |
| Ignoring layer caching | Builds take 10+ minutes | Copy lockfiles first, then source code |
| Skipping Docker Compose for multi-service apps | Developers must start services manually | Define all services in one compose file |
How to Validate Your Strategy Works
A strategy is only useful if it solves real problems. Measure these three metrics before and after implementation.
- Time to onboard a new developer. How long does it take from cloning the repo to running the test suite? A good container strategy should bring this under 15 minutes.
- Environment-related bug reports. Count the number of tickets labeled “environment” or “works on my machine.” This number should drop to near zero.
- Build time in CI. If your CI pipeline builds the same images as your local setup, track the average build duration. Faster builds mean faster feedback loops.
If your numbers improve, the strategy is working. If they do not, revisit the weak leg of the table.
Tools That Complement Your Container Strategy
Your container strategy does not live in a vacuum. It works alongside other Essential Dev Tools for Streamlining Your Development Workflow in 2026. Consider adding:
- Task runners like
makeorjustto wrap common Docker commands. A singlemake devcan start everything. - Volume watchers that sync files into the container when they change. This enables live reload without manual restarts.
- Docker Desktop or OrbStack for local development. Both provide a clean UI for managing containers and debugging network issues.
Making the Strategy Stick
A written strategy is worthless if nobody follows it. Enforce it through automation, not meetings. Add a CI check that verifies the Dockerfile follows your base image standard. Use a linter like hadolint to catch anti-patterns. Create a pull request template that reminds contributors to update the lockfile when they add a dependency.
Your strategy should also evolve. Revisit it every quarter. Ask the team what hurts. Maybe the base image is too large, or the secrets management is too cumbersome. Adjust accordingly. A living strategy beats a perfect, abandoned one.
Your Next Move
Start small. Pick one service that causes the most environment headaches. Write a Dockerfile for it. Create a simple docker-compose.yml. Share it with one teammate and ask them to test it. Fix the issues they find. Then expand to the rest of your stack.
A development environment container strategy is not a luxury. It is the foundation of a predictable, productive engineering culture. Take the first step today, and you will save yourself and your team countless hours of debugging the wrong problems.