alexander
You push code to GitHub a dozen times a day. Each time, you risk exposing an API key, a database password, or a service token. In 2026, the stakes are higher than ever. Attackers have automated bots that scan public repositories for hard-coded secrets within minutes of a push. A single exposed key can lead to a cloud bill shock of tens of thousands of dollars or a full data breach. The solution is simple: use a dedicated secret manager. It is no longer a nice-to-have. It is a core part of any professional development workflow.
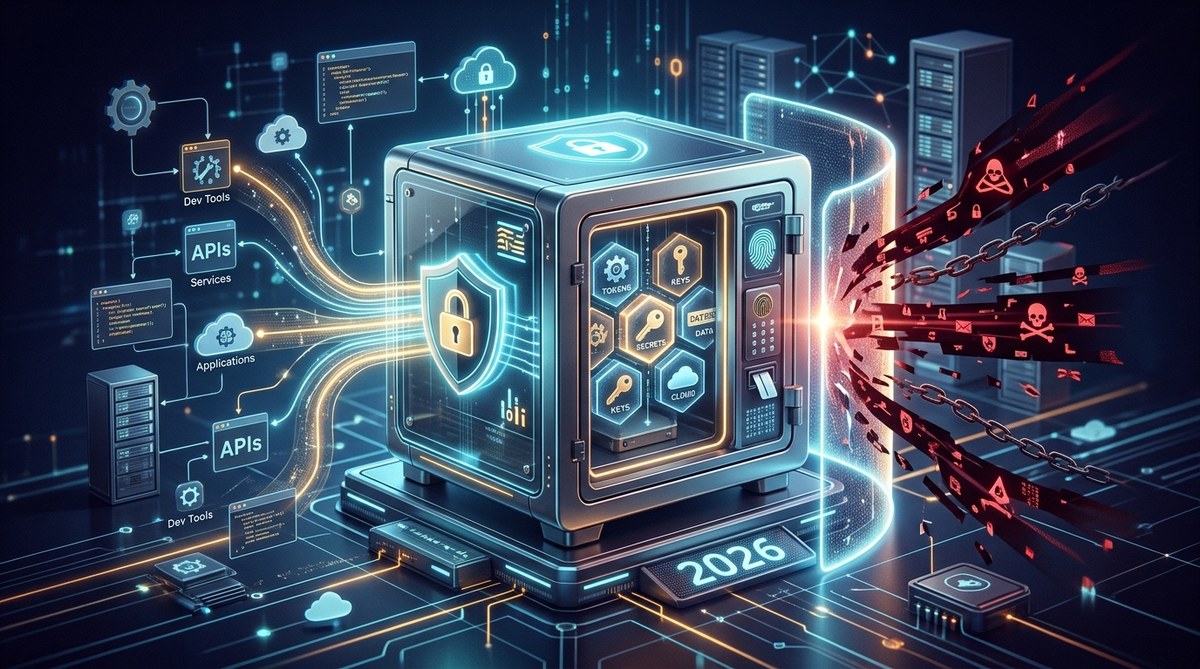
A secret manager centralizes and encrypts your API keys, tokens, and credentials so they never appear in your code, logs, or version control. In 2026, using one is the standard way to prevent credential leaks, automate rotation, and enforce access control across your team. It replaces insecure practices like .env files, hard-coded strings, and shared spreadsheets.
What Makes 2026 Different for Secret Management
The security landscape has shifted. Here is what changed.
First, supply chain attacks are now the most common vector for breaches. When you embed a secret in a configuration file and commit it, you are handing that secret to anyone who forks your repo or downloads your package. Second, cloud costs are more visible. Engineers are held accountable for runaway bills caused by leaked cloud API keys. Third, compliance frameworks like SOC 2 and ISO 27001 now require automated secret rotation and audit trails. You cannot pass an audit by saying you keep secrets in a shared Google Doc.
A secret manager solves all three problems. It acts as a single source of truth for credentials. It encrypts them at rest and in transit. It provides access logs so you know who accessed what and when.
How a Secret Manager Protects Your API Keys and Tokens
A secret manager is not just a password locker. It is a system designed for machine-to-machine authentication. Here is how it works.
When your application needs an API key, it requests it from the secret manager at runtime. The key is never written into a file on disk. It is never in your source code. It is never in your CI/CD logs. The manager returns the value over an encrypted connection, and your application holds it in memory for the duration of the session.
This approach stops the most common leak paths. Developers cannot accidentally commit secrets. Compromised dependencies cannot read secrets from config files. Even if an attacker gains access to your source code, they cannot extract credentials.
The Real Cost of Not Using a Secret Manager
Let us look at what happens without one.
Consider a team that stores API keys in a .env file in the project root. They add .env to .gitignore, but someone on the team renames the file during a refactor. The .gitignore entry no longer matches. The next commit pushes the file to the remote repository. Within minutes, a scanning bot finds the key and starts using it. The team only notices when the cloud provider sends an alert about unusual traffic. By then, the bill has reached thousands of dollars.
This scenario plays out every week. A secret manager prevents it by ensuring the key never touches a file in the repository in the first place.
Common Mistakes Developers Make with Secrets
The table below shows frequent errors and how a secret manager helps avoid them.
| Mistake | What Happens | How a Secret Manager Fixes It |
|---|---|---|
| Hard-coding keys in source files | Keys are exposed in version control history | Keys are stored outside the repo entirely |
| Sharing secrets via chat or email | Secrets are stored in unencrypted logs and archives | Secrets are accessed through a controlled API |
| Using the same key across environments | A breach in staging compromises production | Each environment gets its own scope and key set |
| Manual key rotation | Keys are forgotten and remain valid for years | Automated rotation policies enforce expiry |
| Storing secrets in CI/CD environment variables | Anyone with CI access can read them | Secrets are injected at runtime without being stored in CI config |
Setting Up a Secret Manager for Your Team
Getting started is straightforward. Follow these steps.
-
Choose a secret manager that fits your stack. Popular options in 2026 include HashiCorp Vault, AWS Secrets Manager, and open-source tools like SOPS or Infisical. Evaluate based on your infrastructure. If you are all-in on AWS, use AWS Secrets Manager. If you run a multi-cloud or on-prem setup, Vault is a better fit.
-
Install the client library in your application. Most secret managers provide SDKs for Python, Node.js, Go, Java, and other common languages. The library handles authentication and encryption automatically.
-
Define your secrets in the manager. Create entries for each API key, database credential, and service token. Group them by environment: development, staging, production.
-
Replace hard-coded values in your code with calls to the secret manager. For example, instead of
api_key = "sk-abc123", you writeapi_key = vault_client.get_secret("stripe_prod_key"). -
Set up access policies. Restrict who can read and write secrets. Use short-lived access tokens for your applications. Enable audit logging so you can see every access event.
-
Automate rotation. Configure your secret manager to rotate keys on a schedule. Many managers can generate new keys and update dependent services automatically.
Tools to Consider in 2026
The market has matured. Here are the tools worth evaluating.
-
HashiCorp Vault: The gold standard for dynamic secrets. It supports time-based tokens, automatic revocation, and fine-grained access control. It requires some operational overhead to run a Vault cluster.
-
AWS Secrets Manager: The best choice if you are already in the AWS ecosystem. It integrates with Lambda, ECS, and RDS. It handles rotation for database credentials automatically.
-
Google Cloud Secret Manager: Similar to AWS but for GCP users. It offers replication across regions and tight integration with Cloud Run and Cloud Functions.
-
Azure Key Vault: A solid option for Azure shops. It supports hardware-backed encryption and integrates with Azure Pipelines.
-
Infisical: An open-source alternative that runs on your own infrastructure. It is lightweight and easy to self-host. Good for startups that want control without the complexity of Vault.
-
SOPS (Secrets OPerationS): Not a running service but a file encryption tool. It encrypts individual files so you can commit them to version control safely. It works well for small teams but does not provide runtime access or rotation.
Integrating with Your CI/CD Pipeline
Your pipeline is a common place where secrets leak. Many teams set environment variables in their CI/CD tool, but those values are visible to anyone with access to the project settings.
A better approach is to have your pipeline fetch secrets from the manager at build time. Here is a typical flow.
- The CI/CD runner authenticates with the secret manager using an identity token scoped to the pipeline.
- The runner requests only the secrets it needs for that specific job.
- Secrets are injected as environment variables for the duration of the build.
- After the build, the runner discards the secrets.
This pattern ensures that secrets never persist in CI/CD configuration files or logs. It also means you can rotate secrets without updating your pipeline configuration.
What to Do When a Secret is Compromised
Even with a secret manager, breaches can happen. The difference is that you can react instantly.
- Revoke the compromised secret in the manager. This takes one API call.
- Generate a new secret and update the manager entry.
- The next time your application starts a new session, it fetches the new value automatically.
- Check the audit log to see which services accessed the old secret. This helps you understand the blast radius.
Without a secret manager, you would need to find every file and environment where the secret was stored, update them manually, and hope you did not miss one.
The Human Side of Secret Management
Tools are only part of the solution. Your team needs to adopt the right habits.
- Make secret management part of your onboarding. New engineers should learn how to request access and how to use the client library.
- Run regular secret scanning on your repositories. Tools like GitGuardian or truffleHog can catch secrets that slip through.
- Hold a post-mortem after any secret leak. Focus on process improvements, not blame.
- Set up alerts when a secret is accessed from an unusual location or at an unusual time.
These practices build a culture where secret management is normal, not an afterthought.
Why Your Stack is Incomplete Without One
You probably already use a package manager to handle dependencies. You use version control to manage your code. You use a CI/CD tool to automate builds. A secret manager fills the same role for credentials. It is the missing piece that closes a critical gap in your security posture.
In 2026, the tools are mature, the integrations are smooth, and the cost is low. There is no good reason to keep storing API keys in files. Every day you delay is a day your secrets are exposed to unnecessary risk.
Adopting Secret Management as a Standard Practice
Start small. Pick one service, move its key to a secret manager, and update your application to fetch it at runtime. Run that setup for a week. See how it feels. Once you see how painless it is, you will want to move all your secrets.
Your future self will thank you when a security scanner finds nothing in your repository. Your operations team will thank you when a key rotation happens without a deployment. Your compliance officer will thank you when the audit goes smoothly.
A secret manager for API keys and tokens is not a luxury. It is the baseline for professional software development in 2026. Set it up this week. Your applications will be safer, your team will be more productive, and you will sleep better at night knowing your credentials are where they belong.